Adobe today released emergency updates that fix a critical vulnerability for the ColdFusion web app development platform. The bug can lead to arbitrary code execution and has been exploited in the wild. The security issue allows an attacker to bypass restrictions for uploading files. To take advantage of it, the adversary has to be able to upload executable code to a directory of files on a web server. The code can then be executed via an HTTP request, Adobe says in its security bulletin. Critical bug exploited All ColdFusion versions that do not have the current updates are affected by the vulnerability (CVE-2019-7816), regardless of the platforms they are for. Charlie Arehart, an independent consultant credited for reporting the vulnerability, told us that he discovered the bug… Source link
Read More »Update ColdFusion Now, Critical Zero-Day Bug Exploited in the Wild
Adobe today released emergency updates that fix a critical vulnerability for the ColdFusion web app development platform. The bug can lead to arbitrary code execution and has been exploited in the wild. The security issue allows an attacker to bypass restrictions for uploading files. To take advantage of it, the adversary has to be able to upload executable code to a directory of files on a web server. The code can then be executed via an HTTP request, Adobe says in its security bulletin. Critical bug exploited All ColdFusion versions that do not have the current updates are affected by the vulnerability (CVE-2019-7816), regardless of the platforms they are for. Charlie Arehart, an independent consultant credited for reporting the vulnerability, told us that he discovered the bug… Source link
Read More »Update ColdFusion Now, Critical Zero-Day Bug Exploited in the Wild – BleepingComputer

[unable to retrieve full-text content]Update ColdFusion Now, Critical Zero-Day Bug Exploited in the Wild BleepingComputer Source link
Read More »Web Hosting Services Market Is Booming| Namecheap, InMotion
HTF MI recently introduced Global Web Hosting Services Market study with in-depth overview, describing about the Product / Industry Scope and elaborates market outlook and status to 2023. The market Study is segmented by key regions which is accelerating the marketization. At present, the market is developing its presence and some of the key players from the complete study are Namecheap, InMotion Hosting, Hostwinds, Liquid Web, OVH, DigitalOcean, Hostwinds, CPanel, Linode, Vultr, GoDaddy, 1&1, HostGator, TMDHosting, DreamHos, Bluehost, SiteGround, A2 Hosting, etc. Request Sample of Global Web Hosting Services Market Report 2018 @: https://www.htfmarketreport.com/sample-report/1592180-global-web-hosting-services-market-3 This report studies the Global Web… Source link
Read More »How running websites has changed in the last two decades (for an Ars IT guru)
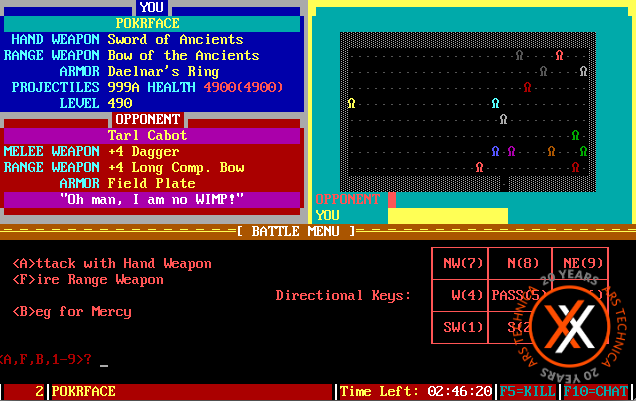
The Pit, a BBS door game. In this shot, Lee Hutchinson was attacking these guys. Or, maybe they’re attacking him. Lee Hutchinson Ars Technica’s 20th Anniversary View more stories I was a true nerd growing up in the 1980s—not in the hipster way but in the 10-pound-issue-of-Computer-Shopper–under-my-arm way (these things were seriously huge). I was thoroughly addicted to BBSes (Bulletin Board Systems) by the time I was 10. Maybe it’s no surprise I ended up as a technical director for a science and tech site. In fact, I’d actually draw a direct line between the job of managing your own BBS (aka SysOping) to managing a modern Web infrastructure. And with everyone around Ars looking back given the site’s 20th anniversary, let’s make… Source link
Read More »New online service will hack printers to spew out spam
After a Twitter user hacked over 50,000 printers last week to promote PewDiePie’s YouTube channel as part of a guerilla marketing campaign, a new service has spawned over the weekend advertising the same type of functionality, but for everyone. Going under the generic term of “Printer Advertising,” this new service claims it can hack printers all over the world to print out messages on demand, similar to the PewDiePie promo hack that took place over the weekend. “We have the ability to reach every single printer in the world,” claims a website launched on Sunday. “Reservations are limited.” The website was promoted by –you guessed it– flyers sent out to everyone’s printers. A copy of this… Source link
Read More »Windows VPS Hosting Review | HostReview.com
Recently patched Adobe ColdFusion bug exploited by Chinese APT
A suspected Chines APT group exploited the recently patched ColdFusion vulnerability in the wild by compromising a vulnerable ColdFusion server after directly uploading a China Chopper webshell. The targeted servers hadn’t been updated with the patch released just two weeks earlier. Volexity researchers observed the active exploitation of the newly patched CVE-2018-15961 flaw, a critical unrestricted file upload bug that could also lead to arbitrary code-execution, in Adobe ColdFusion, despite there being no public details or proof-of-concept code exists, according to a Nov. 8 blog post. “The recent Adobe ColdFusion flaw that has been exploited recently is another example of how quickly malicious actors are to take advantage of recently-patched vulnerabilities,” Justin Jett,… Source link
Read More »ATP Group Attacks ColdFusion Servers
Posted on November 9, 2018 at 6:39 PM A cyberspying group appears to have reversed a security patch from Adobe and currently going after unpatched ColdFusion Servers. According to information gathered by Volexity researchers, a spying group is aggressively hacking into the servers of Adobe ColdFusion and creating backdoors for future attacks. This attack has been ongoing since late September with servers not updated with security patches released by Adobe on September 11. Apparently, the hackers have studied Adobe’s September patches and discovered a means of exploiting the CVE-2018-15961 to its advantage. Categorized as an “unauthenticated file upload,” this weakness allowed this nation-state… Source link
Read More »Patched Adobe ColdFusion Flaw Exploited By APT – Threatpost
The critical vulnerability, which was patched earlier in September, has put ColdFusion servers at risk. An Adobe ColdFusion vulnerability, patched two months ago, was being exploited in the wild by a China-linked APT group, researchers found. The vulnerability, CVE-2018-15961, is a critical unrestricted file upload bug that could also lead to arbitrary code-execution, researchers at Volexity, who discovered the exploitation, said on Thursday. “Volexity recently observed active exploitation of a newly patched vulnerability in Adobe ColdFusion, for which no public details or proof-of-concept code exists,” researchers said in a post. “In the attack detected by Volexity, a… Source link
Read More »